


Using AI Wisely: What to Share and What to Protect

Updated: 41 minutes ago
In the spring of 2023, engineers at Samsung's semiconductor business pasted confidential source code into ChatGPT while looking for help with routine tasks. Within weeks, Samsung barred staff in one of its largest divisions from using generative AI tools on company devices and networks (Gurman, 2023). The episode became a cautionary tale, yet the behavior behind it has only spread. In Microsoft and LinkedIn's 2024 Work Trend Index, 78% of people who use AI at work said they bring their own AI tools to the job, while only 39% had received AI training from their employer (Microsoft, 2024).
Many professionals sense the risk and carry a question they are slightly embarrassed to ask out loud: what is actually safe to type into these tools? The answer becomes far simpler once leaders draw one firm line, which is that business information belongs only in business accounts the organization has approved. With that line in place, AI becomes something teams can use with confidence instead of quiet worry.
Why the Account Matters
When you type into an AI tool, your words are processed and stored on the provider's servers, and the terms that govern them depend on the kind of account you are using. Business plans are built for organizations. OpenAI states that by default it does not train its models on data from ChatGPT Enterprise, ChatGPT Business, or its API platform, and it offers retention controls to qualifying organizations (OpenAI, n.d.-b). Anthropic's commercial offerings, such as its Team and Enterprise plans, sit outside its consumer terms entirely (Anthropic, 2025). Many business plans also let administrators decide who has access, how long data is kept, and what happens to an account when an employee leaves, and they come with contracts that spell out who owns the data.
Personal accounts offer the company none of those protections. Whether conversations are used for training, how long they are kept, and whether reviewers may read them are governed by consumer terms and by settings one employee controls, which can be changed, forgotten, or revisited when terms are updated. Google, for example, notes that human reviewers read a subset of Gemini conversations and asks users not to enter confidential information they would not want a reviewer to see (Google, 2026). The company has no visibility into a personal account, no way to retrieve what is in it, and no contract with the provider, so no configuration makes it appropriate for company work. Any information that belongs to the business, from a client email to a draft strategy memo, should go only into a tool the business has approved.
The Cost of Using Whatever Is Closest
The risk of ignoring this line is measurable. IBM's 2025 Cost of a Data Breach Report found that one in five organizations had experienced a breach involving shadow AI, meaning AI tools employees use without approval. A breach at an organization with widespread shadow AI costs, on average, $670,000 more than one at an organization with little or none. And, only 37% of organizations have policies to manage AI or detect unapproved use (IBM, 2025).
Most of this exposure comes from well-meaning employees reaching for whatever tool is closest at hand. The most useful step a leadership team can take is to provide an approved business plan and ask people to use it for all work, at a cost far below the cleanup after a leak.
Five Categories That Deserve Extra Care
An approved business account is the right home for work, though not a license to share everything. Some information carries legal or contractual duties that call for caution even inside sanctioned tools.
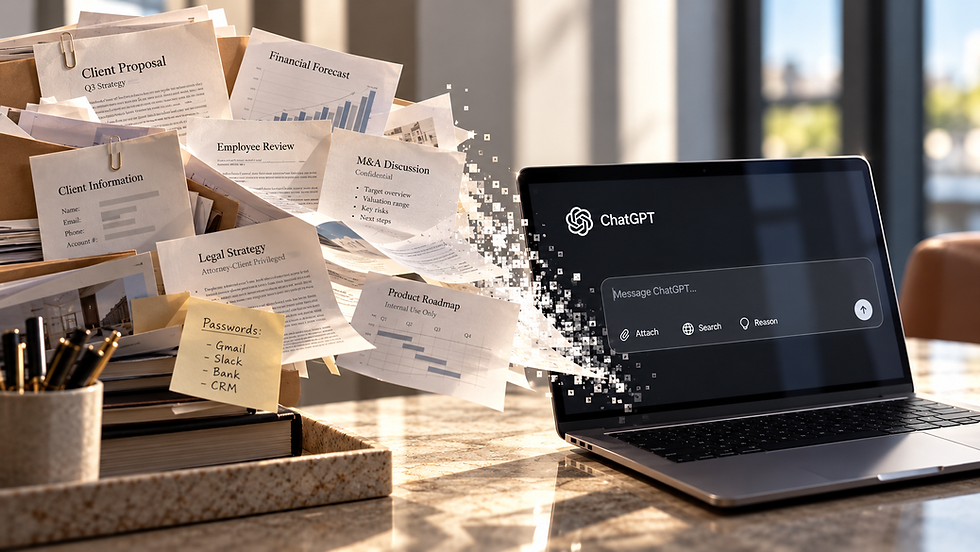
Client and customer details. Names, contact information, account histories, and anything covered by a confidentiality agreement. Confirm that your contracts permit sharing this information with an outside processor, including an approved AI vendor.
Unreleased financial information. Earnings before they are announced, forecasts, pricing plans, and anything related to a pending deal. Information like this can move markets and carries legal duties, so keep it within the tools and people cleared to handle it.
Personnel matters. Performance reviews, pay, health information, complaints, and investigations. Few things damage trust inside a company faster than learning that an employee's private situation traveled further than it needed to.
Passwords and account numbers. Login details, access codes, and bank or card numbers have no place in any AI chat, however secure.
Legal matters. Advice from counsel, active disputes, and settlement terms. Sharing them can raise questions only your lawyers can fully weigh, so ask them first.
Even within an approved tool, share only what the task requires. Replace names with roles, such as "Client A" or "the regional director," round the numbers, and describe the situation in general terms. A model can help you plan a hard conversation with an underperforming manager without ever learning who that manager is, and the advice will be nearly as good.
Put the Line in Writing
Every leadership team benefits from a one-page, plain-language AI policy that names the approved tools, states that work information goes only into them, identifies the categories that need extra care, and tells employees whom to ask when they are unsure. Such policies work best when presented as permission, since people readily follow rules that come with a safe, approved way to get their work done.
Samsung's engineers were trying to do their jobs well, and the rules about what was off limits arrived only after the leak. A clear rule that business information lives in business accounts, delivered from the top and backed by the right tools, removes the quiet worry that keeps many people from using AI at all. It also protects the trust your clients and employees have placed in you, which is worth far more than any time saved.
A Note on Personal Accounts
Personal AI accounts remain useful for everyday life, from planning a trip to working through a household budget, and a few points are worth keeping in mind when you use them.
Check your training setting. Anthropic lets people on its personal Claude plans choose whether their chats help train future models, and it keeps those chats for up to five years when training is allowed, compared with 30 days when it is not (Anthropic, 2025). ChatGPT's equivalent is a setting called "Improve the model for everyone" (OpenAI, n.d.-a).
Use temporary chats for sensitive questions. OpenAI's temporary chats are excluded from training and kept for up to 30 days for safety purposes (OpenAI, n.d.-a), while Gemini holds temporary chats for 72 hours (Google, 2026).
Assume a person may read it. Google keeps chats selected for human review for up to three years, even after you delete your activity (Google, 2026), so share personal health, financial, and family details with care.
Delete what you no longer need. Anthropic does not use deleted conversations for future training (Anthropic, 2025).
References
Anthropic. (2025, August 28). Updates to consumer terms and privacy policy. https://www.anthropic.com/news/updates-to-our-consumer-terms
Google. (2026, September 24). Gemini Apps privacy hub. Gemini Apps Help. https://support.google.com/gemini/answer/13594961
Gurman, M. (2023, May 2). Samsung bans staff's AI use after spotting ChatGPT data leak. Bloomberg. https://www.bloomberg.com/news/articles/2023-05-02/samsung-bans-chatgpt-and-other-generative-ai-use-by-staff-after-leak
IBM. (2025, July 30). IBM report: 13% of organizations reported breaches of AI models or applications, 97% of which reported lacking proper AI access controls [Press release]. https://newsroom.ibm.com/2025-07-30-ibm-report-13-of-organizations-reported-breaches-of-ai-models-or-applications,-97-of-which-reported-lacking-proper-ai-access-controls
Microsoft. (2024, May 8). Microsoft and LinkedIn release the 2024 Work Trend Index on the state of AI at work. Microsoft Source. https://news.microsoft.com/source/2024/05/08/microsoft-and-linkedin-release-the-2024-work-trend-index-on-the-state-of-ai-at-work/
OpenAI. (n.d.-a). Data controls in ChatGPT. OpenAI Help Center. Retrieved October 8, 2026, from https://help.openai.com/en/articles/7730893-data-controls-in-chatgpt
OpenAI. (n.d.-b). Business data privacy, security, and compliance. Retrieved October 8, 2026, from https://openai.com/business-data/
Copyright © 2026 by Severin Sorensen. All rights reserved.


Comments